Email Privacy
Enter a URL
Email Privacy Checker
Every email carries more than the subject line and body.
Hidden in the headers is technical information about where the message came from, which servers handled it, and whether authentication checks passed.
This free tool helps you read those headers in plain language.
How to Use It
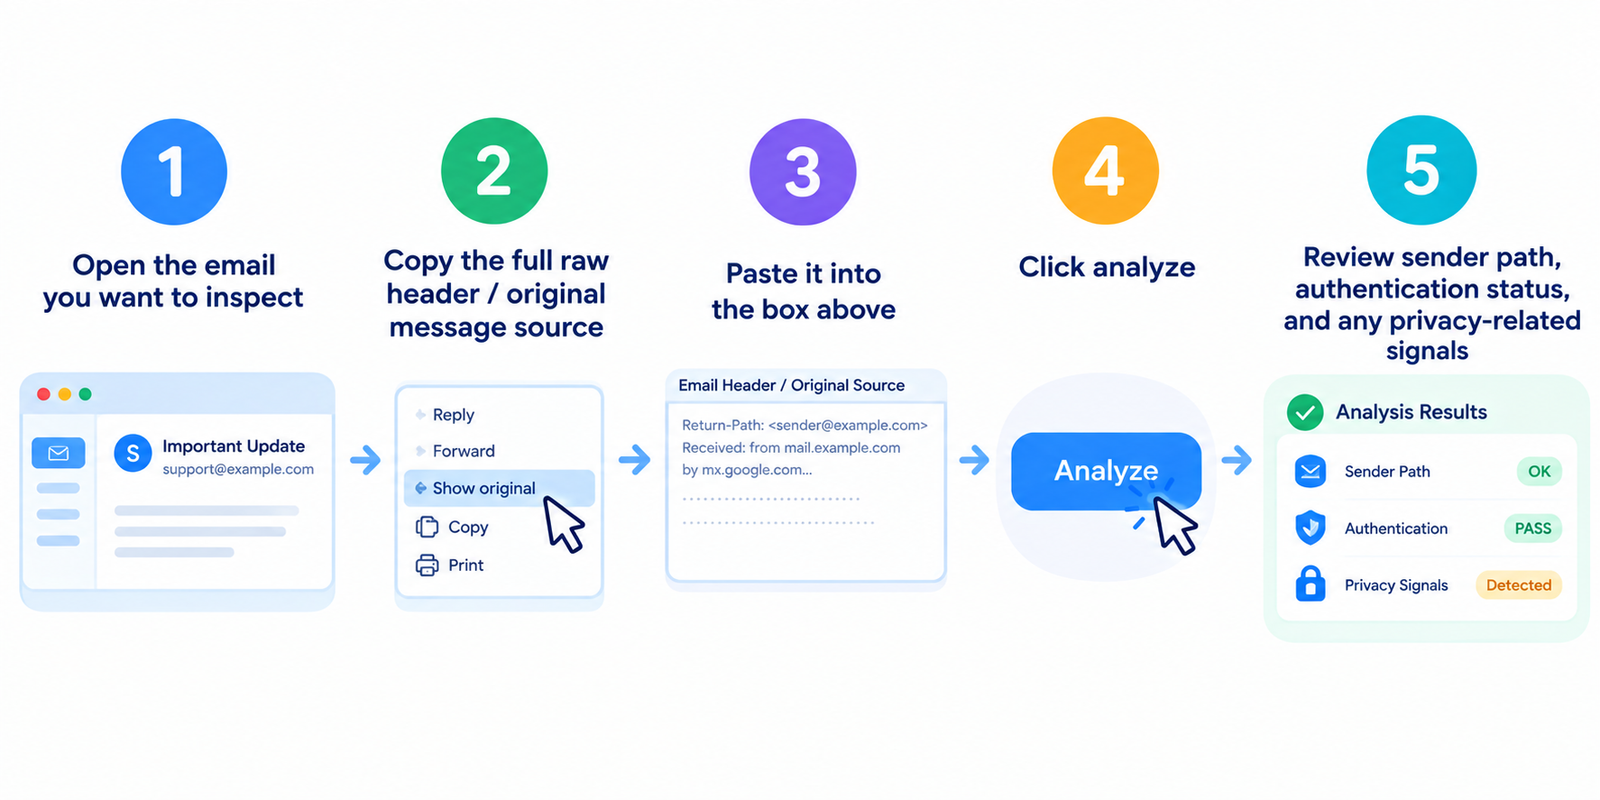
- Open the email you want to inspect
- Copy the full raw header / original message source
- Paste it into the box above
- Click analyze
- Review sender path, authentication status, and any privacy-related signals
How to open headers in common apps
- Gmail: Open email → three dots → Show original
- Outlook on the web: Open email → three dots → View → View message source
- Outlook desktop: Open email → File → Properties → Internet headers
- Yahoo Mail: Open email → More → View raw message
- Apple Mail: View → Message → Raw Source
- Thunderbird: Open email → Ctrl+U (Windows/Linux) or Cmd+U (Mac)
Copy everything from the header block for the most complete analysis.
What Email Headers Can Reveal
| Detail | Why it matters |
|---|---|
| Received path | Shows the server hops the message took |
| Sender-related IPs | May indicate origin network (often hidden by major providers) |
| From / Reply-To | Helps spot mismatches used in phishing |
| SPF / DKIM / DMARC | Shows whether the message authenticated for the claimed domain |
| Message-ID | Unique technical identifier for the message |
| Tracking clues | Some messages include open/click tracking mechanisms |
Headers are technical by design. The goal of this tool is to make the important parts easier to interpret.
Authentication in Simple Terms
SPF
Checks whether the sending server is allowed to send mail for that domain.
DKIM
Uses a cryptographic signature to help verify the message was authorized by the domain and not altered in transit.
DMARC
Tells receiving systems how to handle failures of SPF/DKIM and supports domain-owner reporting.
If authentication fails on a message that claims to be from a bank, payment service, or your CEO, treat it as high risk until verified through another channel.
Practical Ways to Use Header Analysis
Suspicious messages
Before clicking links or opening attachments, check whether authentication looks legitimate.
Invoice / payment requests
Verify the message path and authentication when payment details suddenly change.
Delivery disputes
Header and delivery traces can help show whether a message reached downstream servers.
Privacy awareness
See what technical metadata is attached to messages you send or receive.
This is a diagnostic aid — not a guarantee that a message is safe or unsafe on its own.
Important Limitations
- Sophisticated attackers can still craft convincing messages
- Major providers (like Gmail) often hide the sender’s personal IP
- Partial header copies lead to incomplete results
- Authentication “pass” does not prove the content is trustworthy
- Always verify sensitive requests through a known official channel
When money, passwords, or personal data are involved, use extra caution even if headers look normal.
FAQ
Is this tool free?
Yes. You can analyze headers without creating an account.
Can headers show someone’s exact home address?
No. At most you may see network-level location clues, and many providers conceal originating IPs.
Does a failed SPF/DKIM mean the email is always a scam?
Not always — misconfigurations happen — but failed authentication on sensitive messages is a serious warning sign.
Can I analyze emails I sent?
Yes. Open the sent message source/headers and paste them the same way.
Should I paste confidential email bodies?
Prefer headers only when possible. Avoid sharing unnecessary private content.
Related tools
Note: Header analysis helps you understand technical metadata and authentication signals. It does not replace careful judgment, official verification, or security best practices.